Kenya's New Konza Cybersecurity Centre Bets on AI as Cyber Threats Surge
AI
Published: 2026-11-18T15:16:25 · Updated: 2026-11-18T14:16:25Z
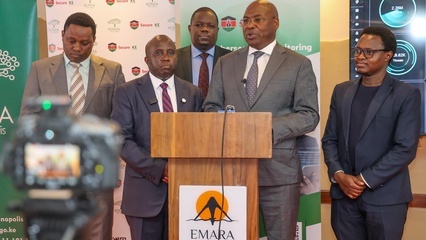
Kenya's expanding digital economy has brought more public services, businesses and citizens online, but it has also created more opportunities for cyberattacks. Government systems, financial institutions and other organisations now have to contend with a range of threats: phishing, ransomware, and attempts to gain unauthorised access to their networks, to name a few. Against this backdrop, the government has launched the SecureKE Sovereign Security Operations Centre at Konza Technopolis. Developed through a partnership involving the Konza Technopolis Development Authority (KoTDA) and SecureKE, the facility is intended to provide continuous cybersecurity monitoring, threat detection and coordinated incident response for government institutions and private organisations. The government says the centre will use AI-enabled analytics to monitor networks, servers, endpoints, cloud environments and applications for potential threats. This initiative is a significant investment towards developing Kenya's cybersecurity infrastructure. But the value it provides will ultimately depend on more than the technology housed at Konza. Organizations will need to use the service effectively, and the centre will have to demonstrate that it can help identify and respond to threats before they cause serious disruption.
A shared approach to cybersecurity
A Security Operations Centre (SOC) brings together the technology, processes and personnel needed to monitor an organization's digital environment, investigate suspicious activity and respond to security incidents. Rather than relying on individual teams to identify and manage every threat independently, a SOC provides a central point for monitoring and analysis. The Konza facility is designed to extend those capabilities to organisations that might not have the resources to establish and maintain their own centres. The government has described the SOC as a shared service that will give public and private sector organisations access to continuous monitoring, threat intelligence, threat hunting, vulnerability management and incident response. The arrangement also has a commercial component to it. While government institutions are enrolled in the service, private organisations will pay an annual fee determined by the infrastructure they want monitored and protected, including assets such as servers, firewalls and routers. These charges will vary according to the scale of each organization's infrastructure. That model of operation could make specialised cybersecurity services more accessible to smaller organisations that would otherwise struggle to recruit dedicated security teams or invest in the technology required to operate their own SOCs. It also offers larger institutions the option of drawing on a centralised service rather than building every capability in-house. However, a shared model would also need to account for the fact that the organizations they serve have different systems, risk profiles and security requirements. Its usefulness will depend on how well the centre can integrate with those environments and provide each organization with actionable information, rather than simply generating alerts.
Kenya's growing cyber threat landscape
This launch is rather timely, coming as reported cyber threat activity in the country continues to rise. It was reported that Kenya recorded 2.7 billion cyber threat events between July and September 2026, representing a 14.45% increase from the preceding quarter. That figure needs to be understood in context: detected threat events include suspicious activity and attempted attacks, and should not be interpreted as billions of successful intrusions or confirmed data breaches. Additionally, the threats are not limited to any one sector. The Communications Authority's cybersecurity reporting has identified government institutions, internet service providers and cloud service providers among the organisations facing significant exposure, with attackers targeting web applications, email systems, network devices and remote access infrastructure. The same reporting recorded more than 44.9 million brute-force attack attempts over the three-month period, which represents an increase of 85.41%. These attacks involve repeated attempts to guess passwords or other access credentials, making weak authentication and poorly secured systems particularly vulnerable. Financial losses offer another indication of the risks facing organisations: reported banking cyber-fraud losses rose to KSh1.9 billion in 2025, up from KSh1.59 billion in 2024. The Central Bank of Kenya also recorded an increase in reported fraud cases, from 353 to 385, while the amount exposed to fraud rose from KSh1.96 billion to KSh2.03 billion. Card fraud losses more than doubled, reaching KSh645.2 million, while losses linked to internet scams rose sharply from KSh6.1 million to KSh86.5 million. These figures do not all describe the same type of cyber incident, but together they illustrate the range of challenges facing Kenya's digital economy, and make it clear that organizations need protection against unauthorised access, financial scams and attacks that could disrupt essential services. That requires more than reacting after an incident has occurred; it calls for proactivity: continuous monitoring and the ability to identify suspicious behaviour early.
Can AI strengthen Kenya's cyber defences?
AI is a central part of the new SOC's offering. Security teams can be confronted with enormous volumes of activity across networks, applications and connected devices, making it difficult to manually review every alert or identify patterns that may indicate an emerging attack. AI-enabled analytics can help process this information, flag unusual behaviour and support the prioritisation of potential threats. At Konza, the government says these capabilities will be applied across networks, servers, endpoints, cloud environments and applications. The centre is also expected to support threat intelligence, proactive threat hunting, vulnerability management and security automation. But AI does not make cybersecurity threats disappear, nor does it eliminate the need for experienced analysts. While automated systems can help identify patterns and surface potential risks, the generated findings still need to be assessed and acted upon. The quality of the underlying data, the accuracy of detection systems and the ability of security teams to distinguish genuine threats from false alarms will all affect how useful the technology is. This is particularly important in a shared environment, where the centre will likely be monitoring systems belonging to organizations with different infrastructure and levels of cybersecurity maturity. The ability to interpret alerts in context and coordinate an appropriate response will matter just as much as detecting unusual activity in the first place.
What the centre needs to deliver
The Konza SOC is also part of a broader effort to establish the technopolis as a hub for Kenya's digital infrastructure. The government has presented locally anchored cybersecurity capabilities as part of its wider digital sovereignty ambitions, with KoTDA highlighting the importance of developing local expertise through training, knowledge transfer and partnerships with academic and technology institutions. That ambition is relevant, but the term sovereign should not be taken to mean that the centre automatically operates without foreign technology or that all data handled through the service necessarily remains within Kenya. The more immediate question is whether Kenya can build and sustain the expertise, operational capacity and institutional oversight needed to protect its digital infrastructure. One of the first tests will be adoption. The centre's effectiveness will depend on how many organizations actually use the service, how much visibility they are willing and able to provide into their systems, and whether the SOC can work with their existing security arrangements. Organizations will also need clarity on data access, confidentiality and responsibility when incidents involve multiple parties. The skills pipeline is also as important. The government has said the initiative will involve training, knowledge transfer and collaboration with academic institutions and technology partners to strengthen local cybersecurity capacity. Those efforts will need to translate into a workforce capable of operating the centre, investigating complex incidents and adapting even as attack methods continue to evolve. Ultimately, the success of the Konza SOC should not be measured simply by the volume of activity it monitors or the number of threats its systems flag. The more meaningful test will be whether it helps organizations detect attacks earlier, respond more effectively and reduce the disruption and financial damage caused by cyber incidents. Kenya has made a substantial investment in the infrastructure. Now the centre has to prove what that investment can deliver.